Codex MCP servers: setup and config
Last checked: 2026-10-14
Codex MCP lets OpenAI Codex discover and call external tools through the Model Context Protocol. Codex can use local stdio servers or remote HTTP servers, including OAuth-protected endpoints. With AIPx, one agent URL exposes the connected account tools that you have permitted for that Codex workflow.
Add an MCP server to Codex
Connect the service accounts in AIPx first. Create an agent for Codex, decide which operations it needs, and copy its personal endpoint. Then register and authenticate the remote server:
codex mcp add aipx --url https://dash.aipx.run/mcp/AGENT_ID
codex mcp login aipx
codex mcp list- Replace AGENT_ID with the dashboard value.
- Complete the browser login opened by the OAuth command.
- Start Codex in the intended project and inspect
/mcp. - Check that the tool list matches your agent’s permitted accounts.
- Ask for one known GitHub issue or Sentry report before trying an operation that changes data.
The CLI registration uses a URL because AIPx is hosted. A local server registration instead describes the command that starts its process. Do not interchange those configurations or supply an upstream account key as if it were the AIPx MCP credential. OpenAI’s Codex MCP documentation covers remote transport and login.
For a first connection, keep the task narrow: retrieve the acceptance criteria for a named issue and report which account supplied them. That verifies the endpoint, authentication, account access and a useful tool call without creating an unintended write.
Codex MCP config: config.toml
Codex declares servers in TOML, rather than the mcpServers JSON used by several other clients. A minimal AIPx entry looks like this:
[mcp_servers.aipx]
url = "https://dash.aipx.run/mcp/AGENT_ID"
The user configuration is ~/.codex/config.toml. Trusted projects can also use .codex/config.toml. The CLI, IDE extension and supported desktop surfaces share the configuration model documented by OpenAI. Inspect the active project and configuration before diagnosing a server that appears in one session but not another.
A project file can communicate which endpoint the repository expects. Authentication is still personal. Never commit access tokens or upstream API keys beside the URL. The endpoint identifies an agent; the OAuth flow grants the client access to that endpoint. If teammates have separate AIPx accounts or task permissions, each may need a different agent declaration.
TOML section names and quoting matter. A mcpServers object pasted from Cursor is not valid Codex configuration. Keep the Codex-specific file and use Cursor’s setup guide or Claude Code’s configuration guide when configuring those clients. Sharing a server does not make their configuration syntax interchangeable.
OpenAI Codex MCP support
Codex supports external tool servers through stdio and Streamable HTTP, with OAuth for compatible remote servers. This is a capability of the client, separate from whether any particular service offers an MCP server. A REST API needs an adapter or a supported integration before Codex can use it as MCP tools.
| Connection | What Codex needs | Typical fit |
|---|---|---|
| Local stdio | A runnable command and its arguments | Tools close to local files or a private environment |
| Remote HTTP | A reachable endpoint and supported authentication | Hosted app integrations |
| AIPx remote agent | The agent URL and OAuth login | Several accounts with different tool rules |
A compatible transport is only the first check. The server must expose useful tool descriptions, input schemas and operations that your account can actually call. A client can connect successfully while particular tools remain hidden or the upstream provider denies access. Inspect each layer rather than assuming an MCP connection grants all service privileges.
Codex as an MCP client
When you add an external server to Codex, Codex is the client. It requests the tool list, chooses calls during the task and receives results. The upstream system remains responsible for executing its operations and enforcing its own account access.
codex mcp-server refers to a different direction: it exposes Codex to another MCP host. It is not the command for adding GitHub, Linear or AIPx to your Codex session. This distinction is useful when a search result says “Codex MCP server” but shows instructions for controlling Codex from a different application.
For ordinary coding work, leave the local repository operations with Codex’s existing tools. Connect an external server for the information outside the checkout: issue requirements, production errors, analytics evidence or service administration. After reading that context, Codex still needs to run the project’s checks before you trust a proposed fix.
Best MCP servers for Codex
Pick integrations according to the missing evidence in your development loop. Each link below covers its connection and tool boundary; the curated MCP server list supplies a wider comparison.
| Integration | Useful input to a coding task | Access decision |
|---|---|---|
| GitHub | Issues, pull requests and repository context | Confirm mutations to the shared repository |
| Linear | A live issue brief and acceptance criteria | Start with reading assigned work |
| Sentry | Errors and their diagnostic context | Limit to the relevant project |
| PostHog | Evidence about feature behavior | Review analytics data exposure |
| Supabase | Database and project context | Use read-only project restrictions where possible |
| Cloudflare | Infrastructure context | Inspect available administrative tools |
| Jira | Requirements from a ticket | Hide unrelated projects or accounts |
| Confluence | Technical decisions and documentation | Keep document writes on Confirm |
| Notion | Product notes behind implementation work | Review workspace access |
| Google Sheets | Test matrices or rollout checklists | Confirm cell changes |
| Stripe | Billing integration context | Restrict financial write operations |
| Gmail | A requested work discussion | Hide personal mail from the coding agent |
For a small repository, GitHub, Linear and Sentry may cover most external context. Adding calendar, health or payments tools without a relevant task increases what the agent can discover without improving the fix. A direct vendor server may be the best choice if you need only that vendor and prefer its native setup.
Give Codex scoped access
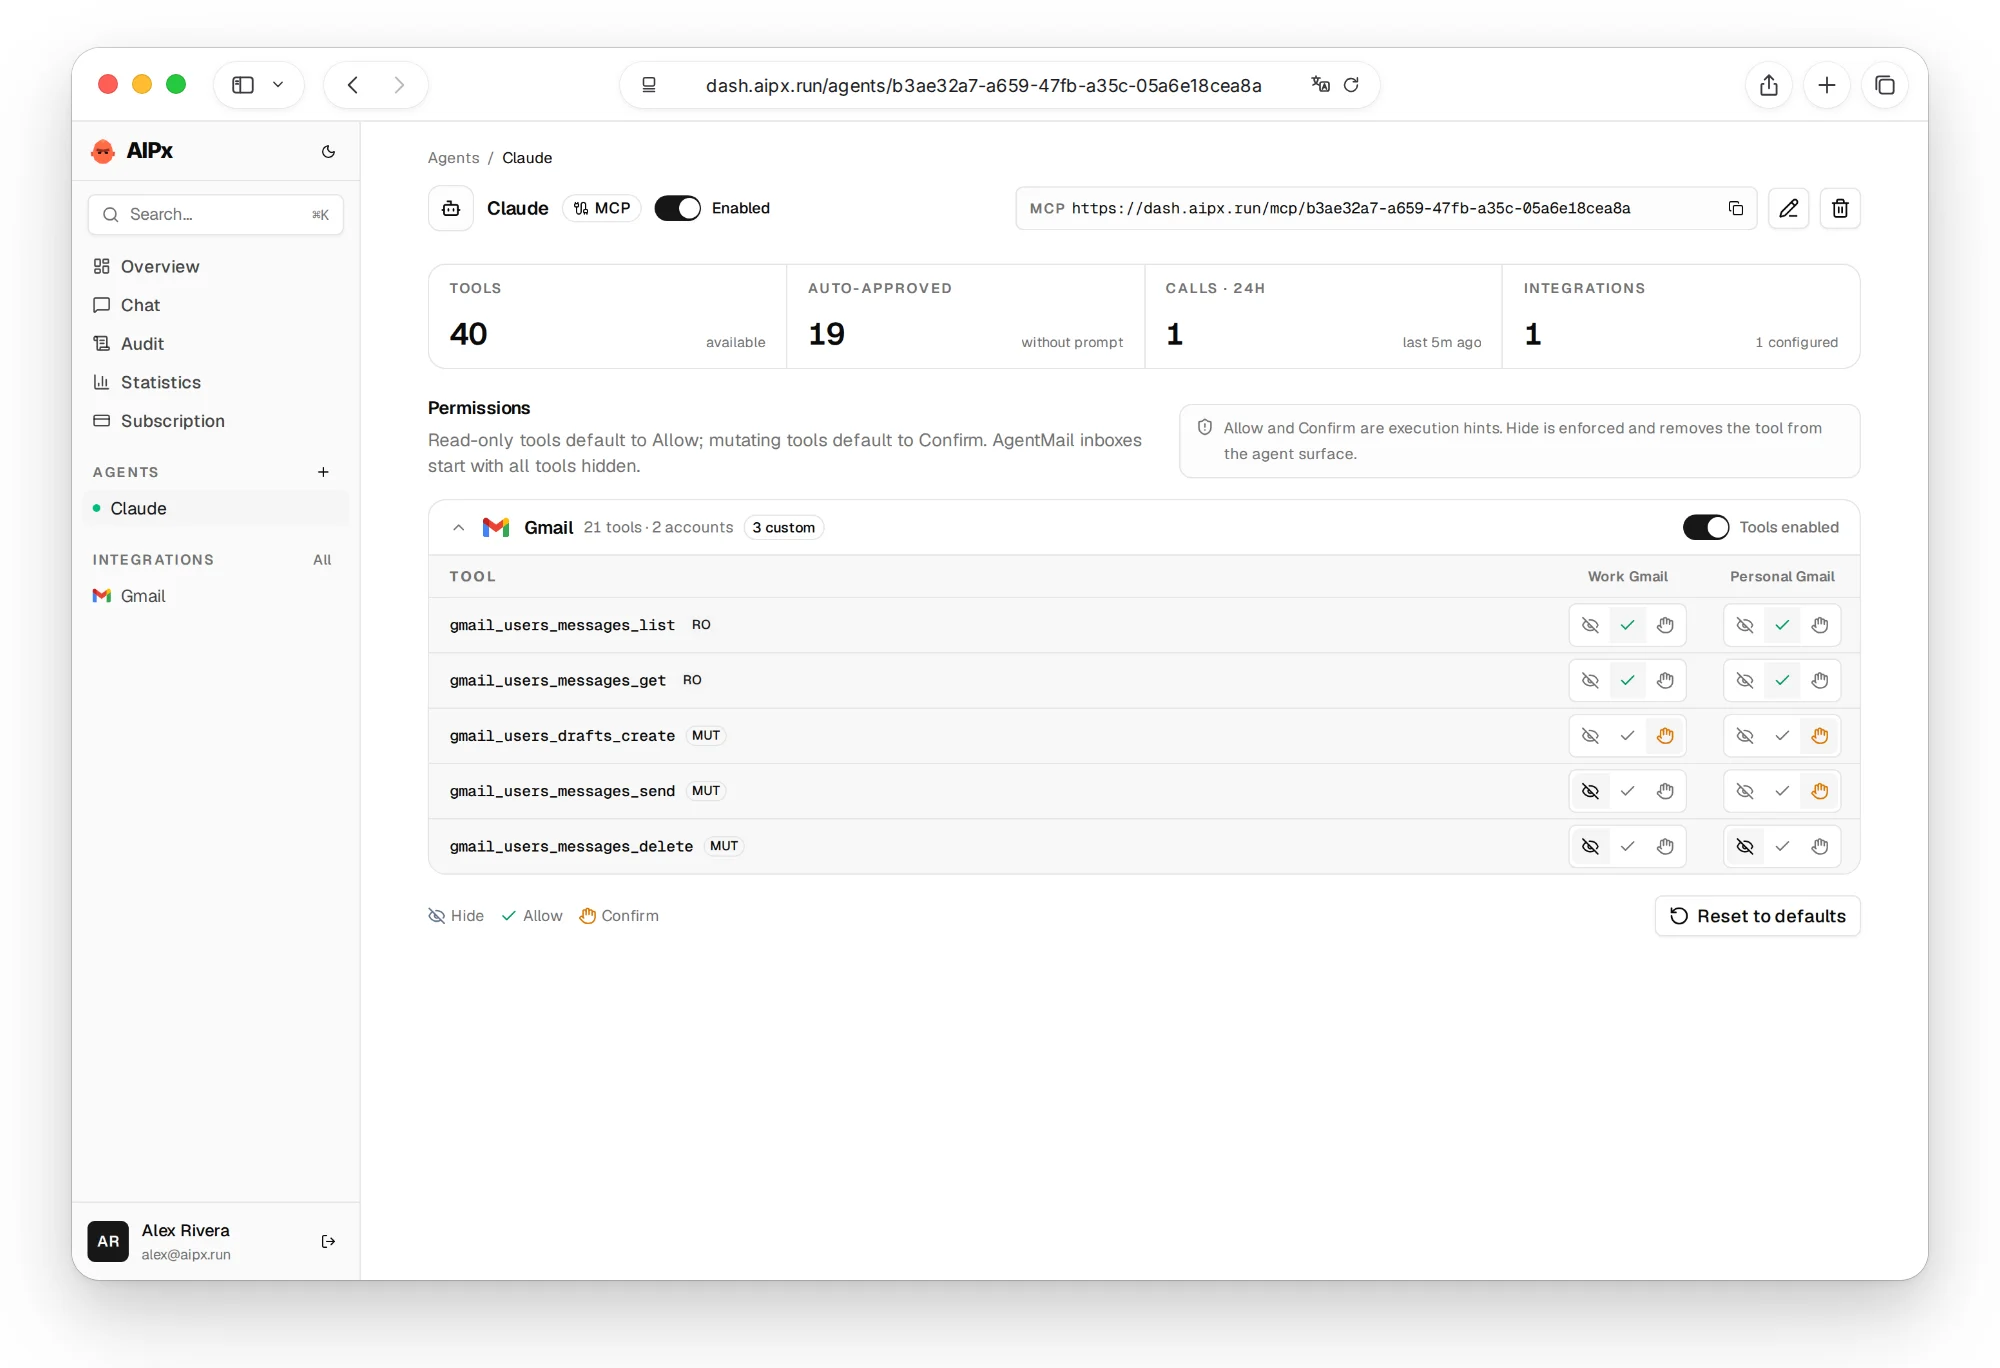
In AIPx, rules combine the agent, connected account and tool. A code-maintenance agent can read the work tracker, ask for confirmation before opening an issue, and have no access to a personal account. Another agent can use the same connected account with different rules.
Allow and Confirm are execution hints, with Confirm requesting client-side review. Actual confirmation depends on the client; Hide is enforced server-side and withholds the operation for that agent. Review reads as well as writes. A read of customer records or private mail can disclose data to the conversation even though it changes nothing upstream. AIPx’s defaults cannot know your confidentiality requirements.
The audit records account, agent, tool, parameters, result and time. Review the first task there, especially if several accounts have similar names. Codex’s own approval and sandbox controls remain relevant to local execution; gateway permission rules govern the external account tools. The MCP gateway guide explains how those accounts are shared across clients.
Troubleshooting Codex MCP
If a server is absent, check the TOML table, project trust and active configuration. If login fails, repeat codex mcp login aipx and verify that the browser signs into the intended AIPx account. If the connection works but a tool is absent, review the agent’s Hide rules and refresh discovery. If the provider rejects a call, reconnect or narrow the upstream account access instead of guessing at a client token.
AIPx adds another hosted operator and depends on network and provider availability. It is not a deployment target for your own local process. Prefer a local server when the tool must remain in a private environment.
Connect your tools to Codex
Beyond the development shortlist, these supported services can supply infrastructure, meeting or specialist context. Keep personal accounts separate from the coding agent unless the task explicitly needs them.
- Development and infrastructure: Atlassian Rovo tools, DigitalOcean infrastructure.
- Mail, notes and planning: Google Calendar events, Apple Calendar access, Things 3 tasks, Granola meeting notes, Fireflies transcripts, AgentMail inbox tools.
- Payments: Paddle subscription tools.
- Research and campaign data: Exa web search, Google Maps data, X account tools, Yandex Direct campaigns.
- Personal health and nutrition: WHOOP recovery data, Withings measurements, Hevy workouts, Numon nutrition reports.
Free includes three connected accounts and one agent. Pro is $3 per month with unlimited connected accounts and agents plus Pro integrations; upstream subscriptions and API limits still apply. Connect free.
FAQ
Does OpenAI Codex support MCP?
Yes. Codex supports local stdio and remote Streamable HTTP servers, including compatible OAuth authentication. An individual server still needs to expose tools your account is permitted to call.
How do I add an MCP server to Codex?
Register the endpoint with codex mcp add, using --url for a remote server. For AIPx, authenticate with codex mcp login aipx and inspect the connection before attempting a write.
Where is Codex MCP config stored?
The user configuration is ~/.codex/config.toml, with project configuration available in .codex/config.toml for trusted projects. Servers use named mcp_servers tables.
How do I authenticate an OAuth MCP server in Codex?
Run codex mcp login with the registered server name and complete browser sign-in. The AIPx OAuth credential is separate from the authorization connecting AIPx to your service account.
Is Codex an MCP client or an MCP server?
It can play either role in different workflows. Adding external servers makes Codex the client; codex mcp-server exposes Codex to another host. Those commands configure opposite directions.